



Simple password leads to data breaches in Denmark
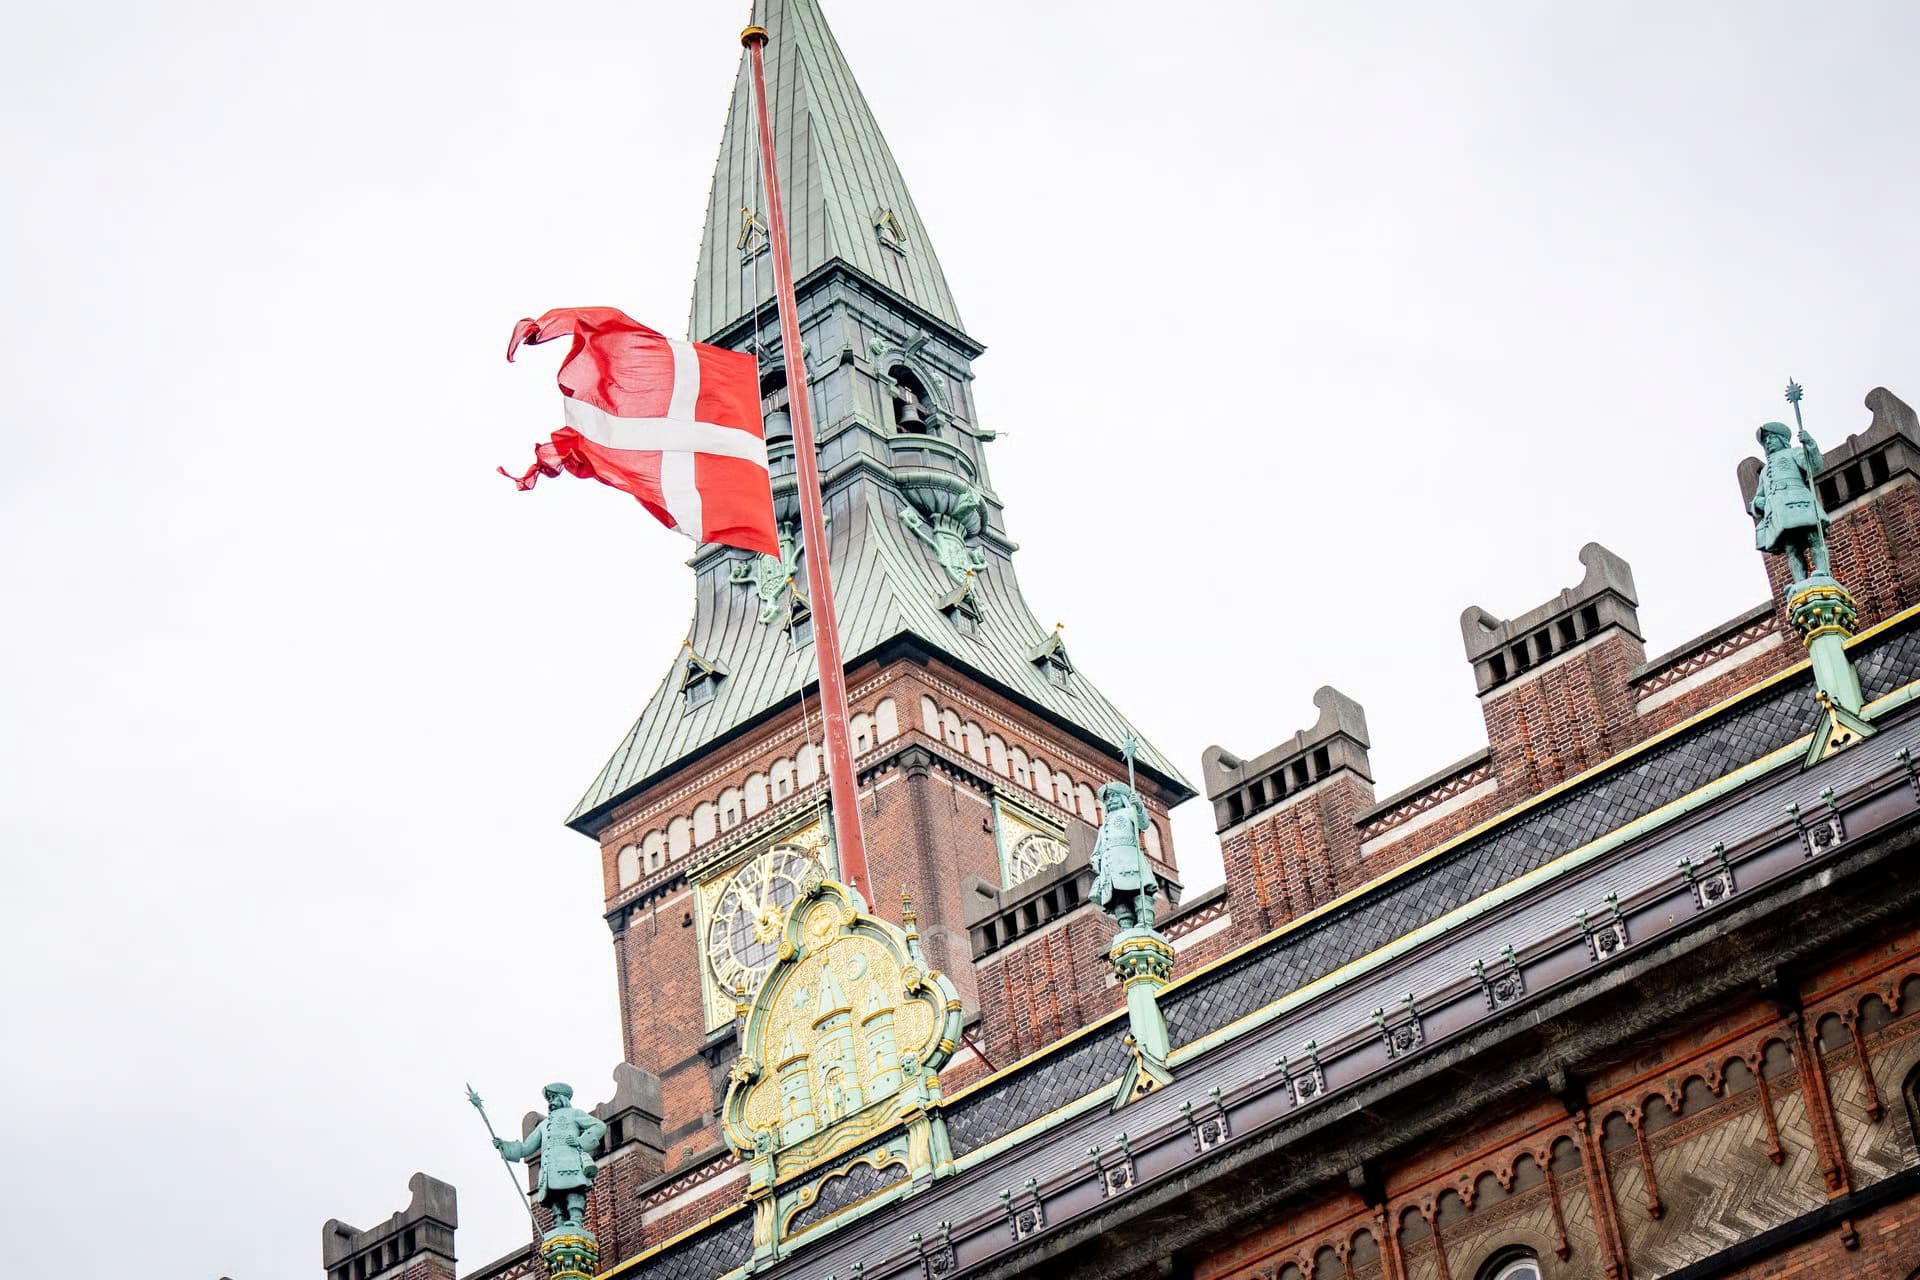
Personal data of nearly 8.8 million people in Denmark has been leaked through a breach of the Central Population Register (CPR) database system. Hackers exploited the credentials of Pays ApS using weak accounts with the password "123456," allowing them to access data and carry out approximately 14 million automated search queries in a short period. The breach resulted in the leak of names, addresses, ID numbers, and led to the company's website being taken offline. The hackers apparently did not intend to sell or publish the data. Authorities confirmed that the attacker exploited legitimate channels unlawfully, highlighting the vulnerability of password security in institutions handling sensitive information.
تنويه: هذا ملخص تم إنشاؤه بواسطة الذكاء الاصطناعي
comments.heading