15 Hrs
Source:
شبكة راية الإعلامية
شبكة راية الإعلامية
Ready to play
Ready to play
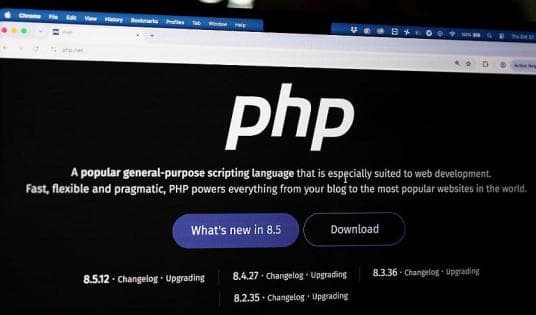
Security reports have revealed the use of two serious vulnerabilities in the PHP programming language, allowing attackers to execute remote code without the need for login credentials. This has led to the suspension of governmental and banking institutions in several countries, most notably Japan and Finland, as precautionary measures. Organizations have accelerated their efforts to update their systems and implement software patches, as companies like Cloudflare and Amazon have issued warnings about increasing attempts to exploit these vulnerabilities. The issues relate to memory management flaws and internal data processing errors, which can be exploited to carry out attacks without authentication. Development teams have advised institutions to install the latest updates released by PHP, specifically versions 8.5.12, 8.4.27, 8.3.36, and 8.2.35, to close these security gaps. It is also recommended that organizations thoroughly check their systems and conduct security scans, particularly those still operating with older versions of PHP, to prevent any prior exploitation of these vulnerabilities before applying the updates.
Notice: This Is an AI-Generated Summary




Comments (0)